01 / 03
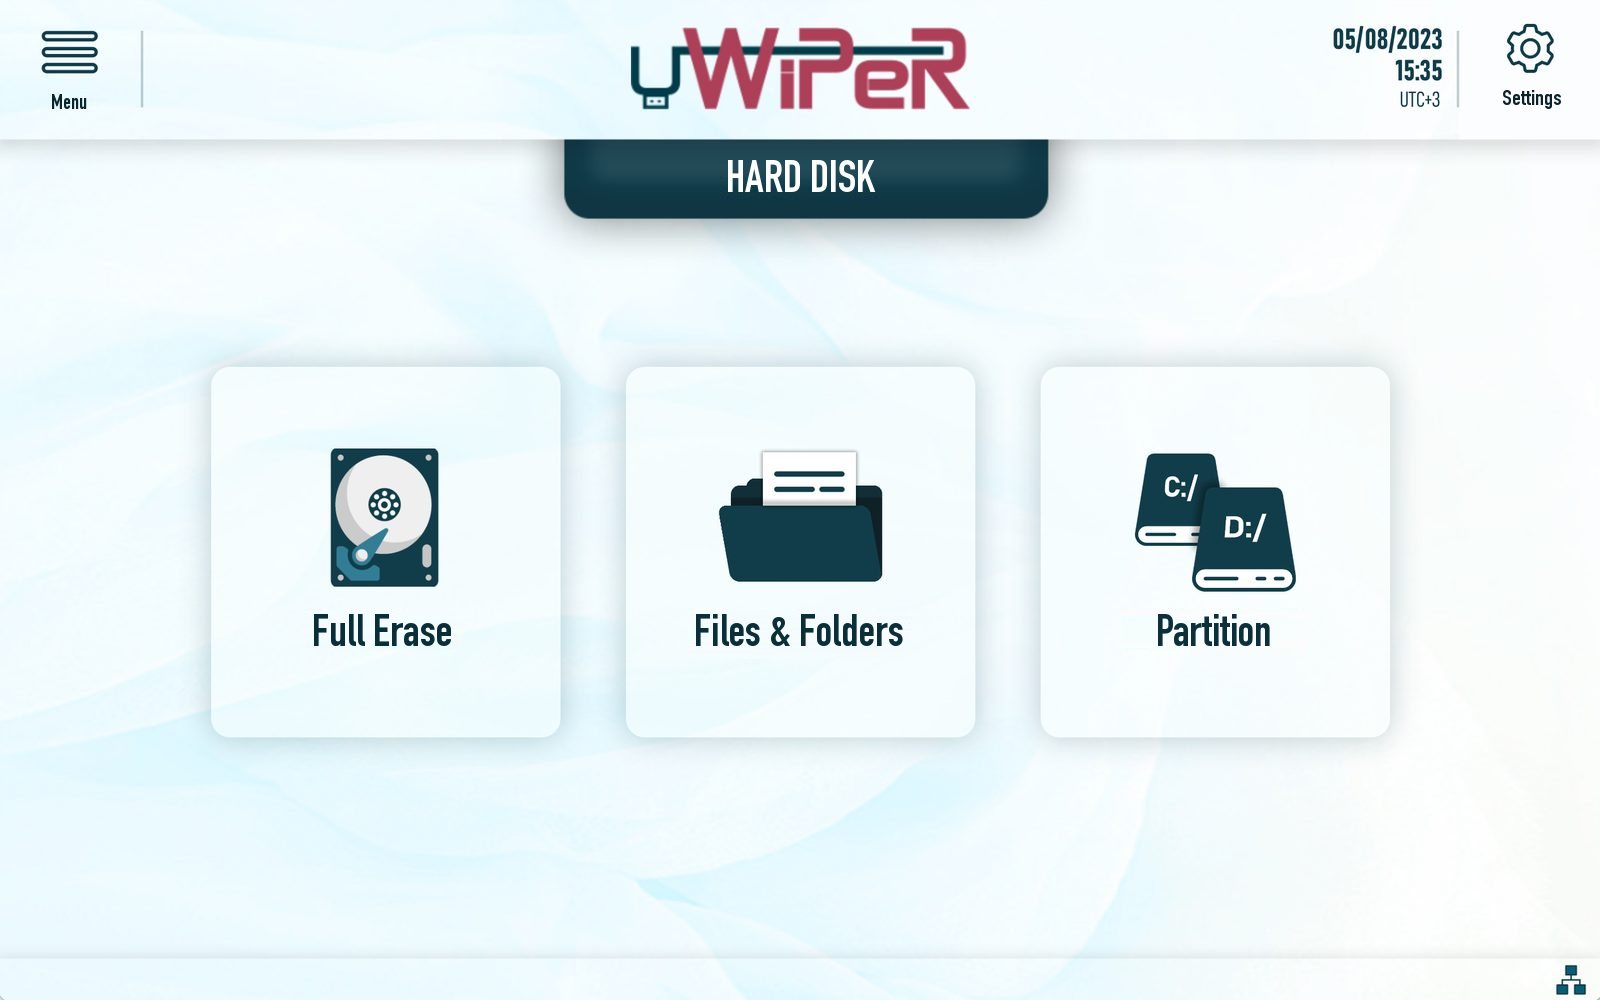
Full disk
Bit‑by‑bit overwrite of the entire drive, with hidden HPA/DCO areas removed on request.
uWiPeR erases disks, SSDs, USB drives and now Android & iOS phones to international standards, verifies the result, tests phone hardware and hands you an audit‑ready report for every single job.
A deleted file is a missing signpost, not missing data. Auditors, regulators and courts don't ask whether someone pressed delete; they ask for evidence. uWiPeR turns every erasure into a record you can show.
Delete only removes the entry in the file table. Every byte is still on the disk, and free tools bring it back in minutes.
Connect up to four 2.5″ / 3.5″ HDDs, SSDs or USB drives, hot‑swap, and erase them at the same time. No PC, no installation, no training.
Bit‑by‑bit overwrite of the entire drive, with hidden HPA/DCO areas removed on request.
Erase only what must go and keep the rest of the drive in service. The report lists every item.
Pick a partition and erase it to standard while the other partitions stay intact.
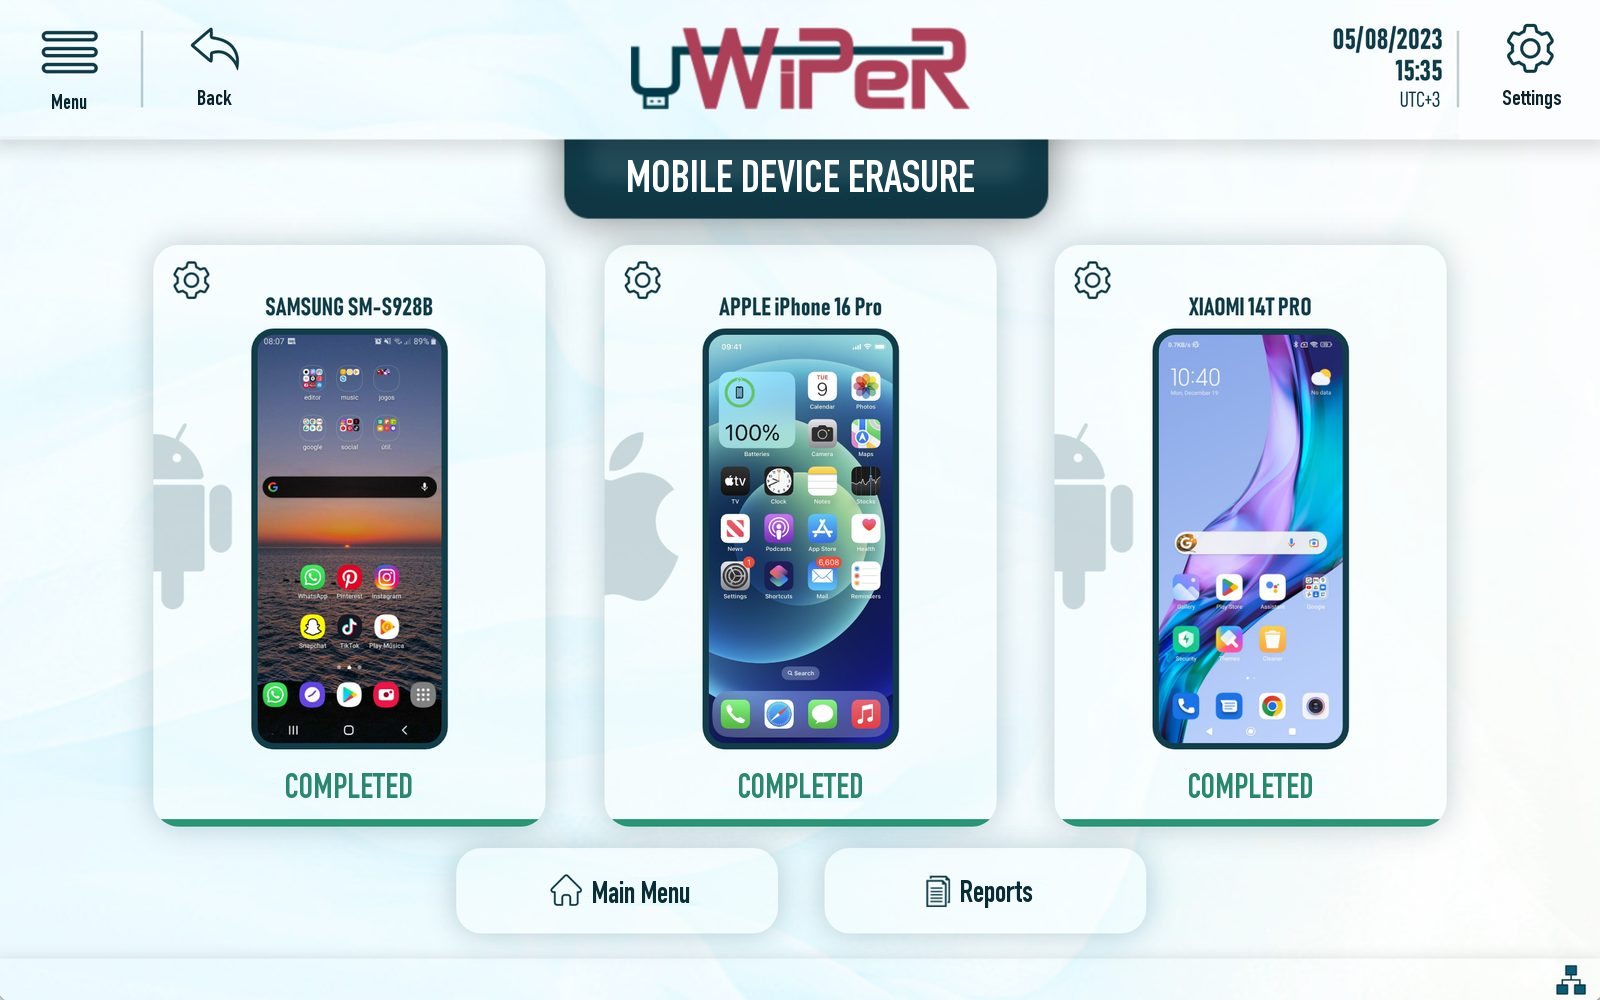
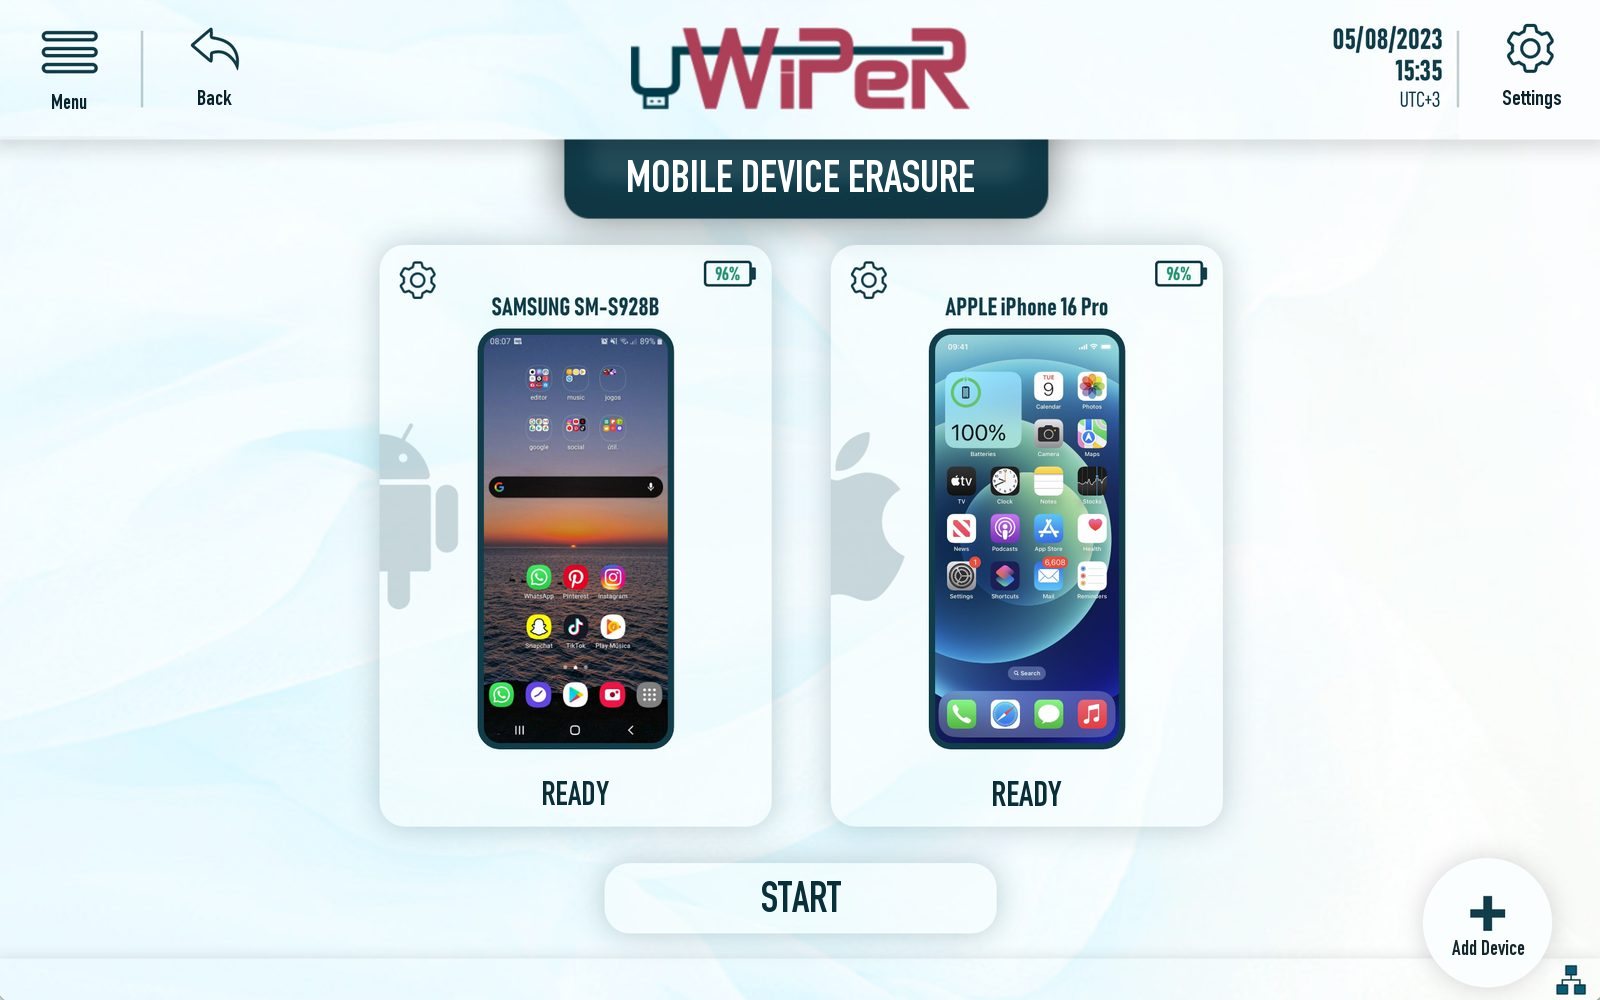
Plug Android and iOS phones straight into uWiPeR and erase several of them side by side. Before anything starts, the device checks what could block a clean, provable erasure.
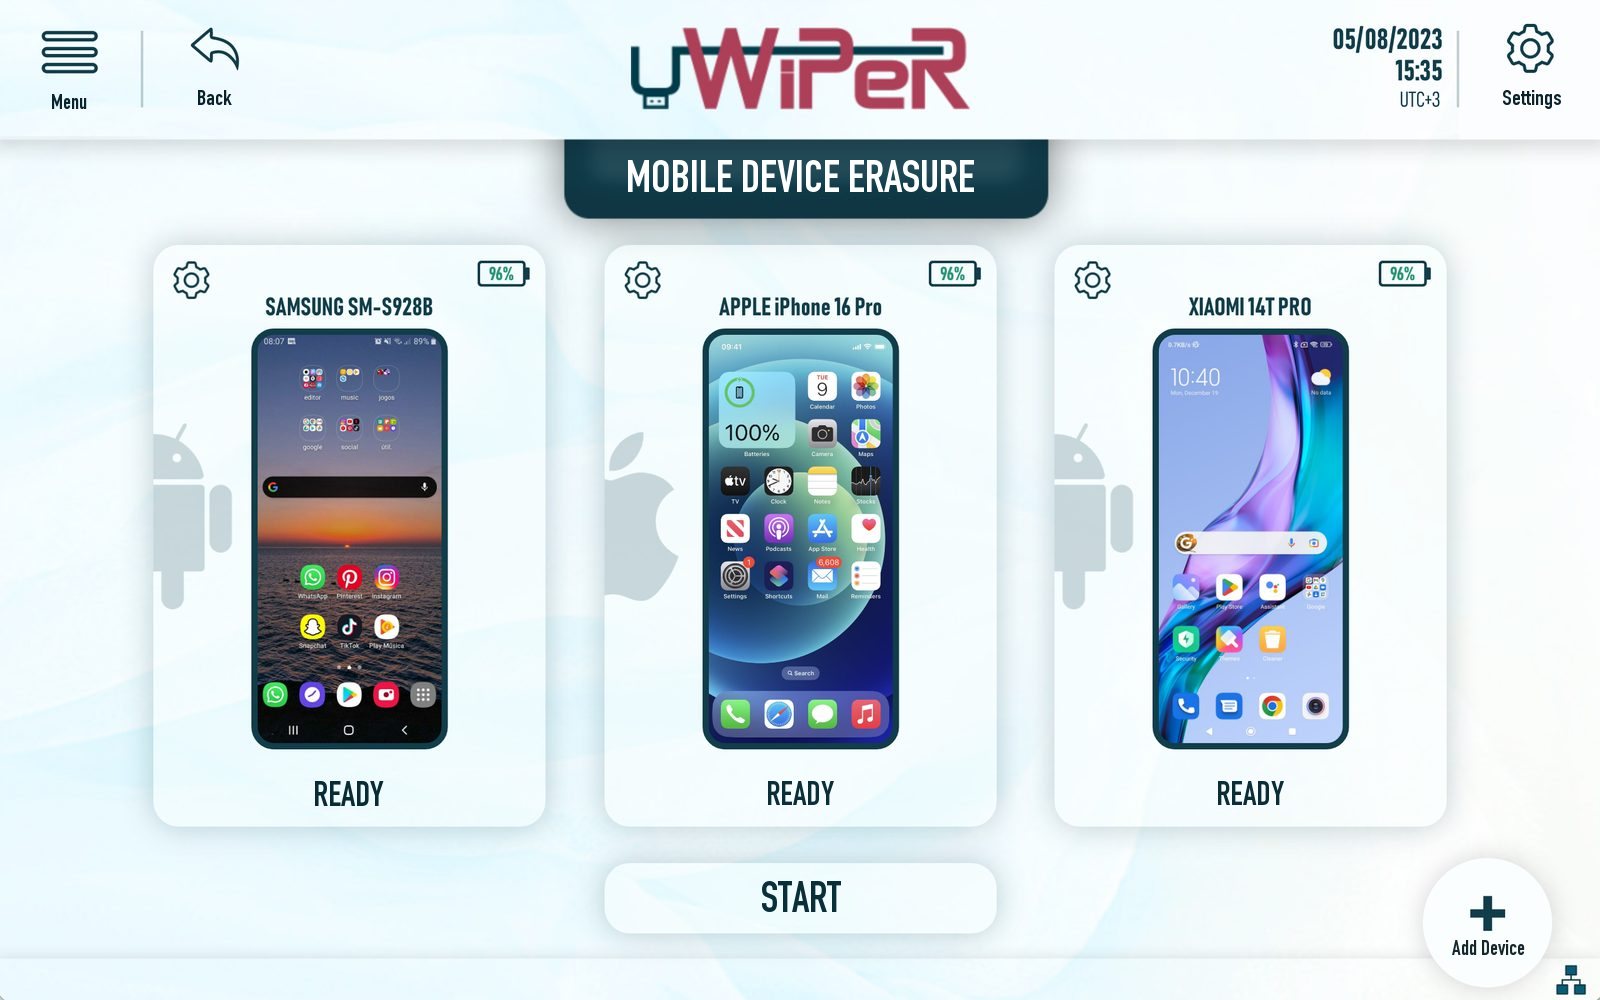
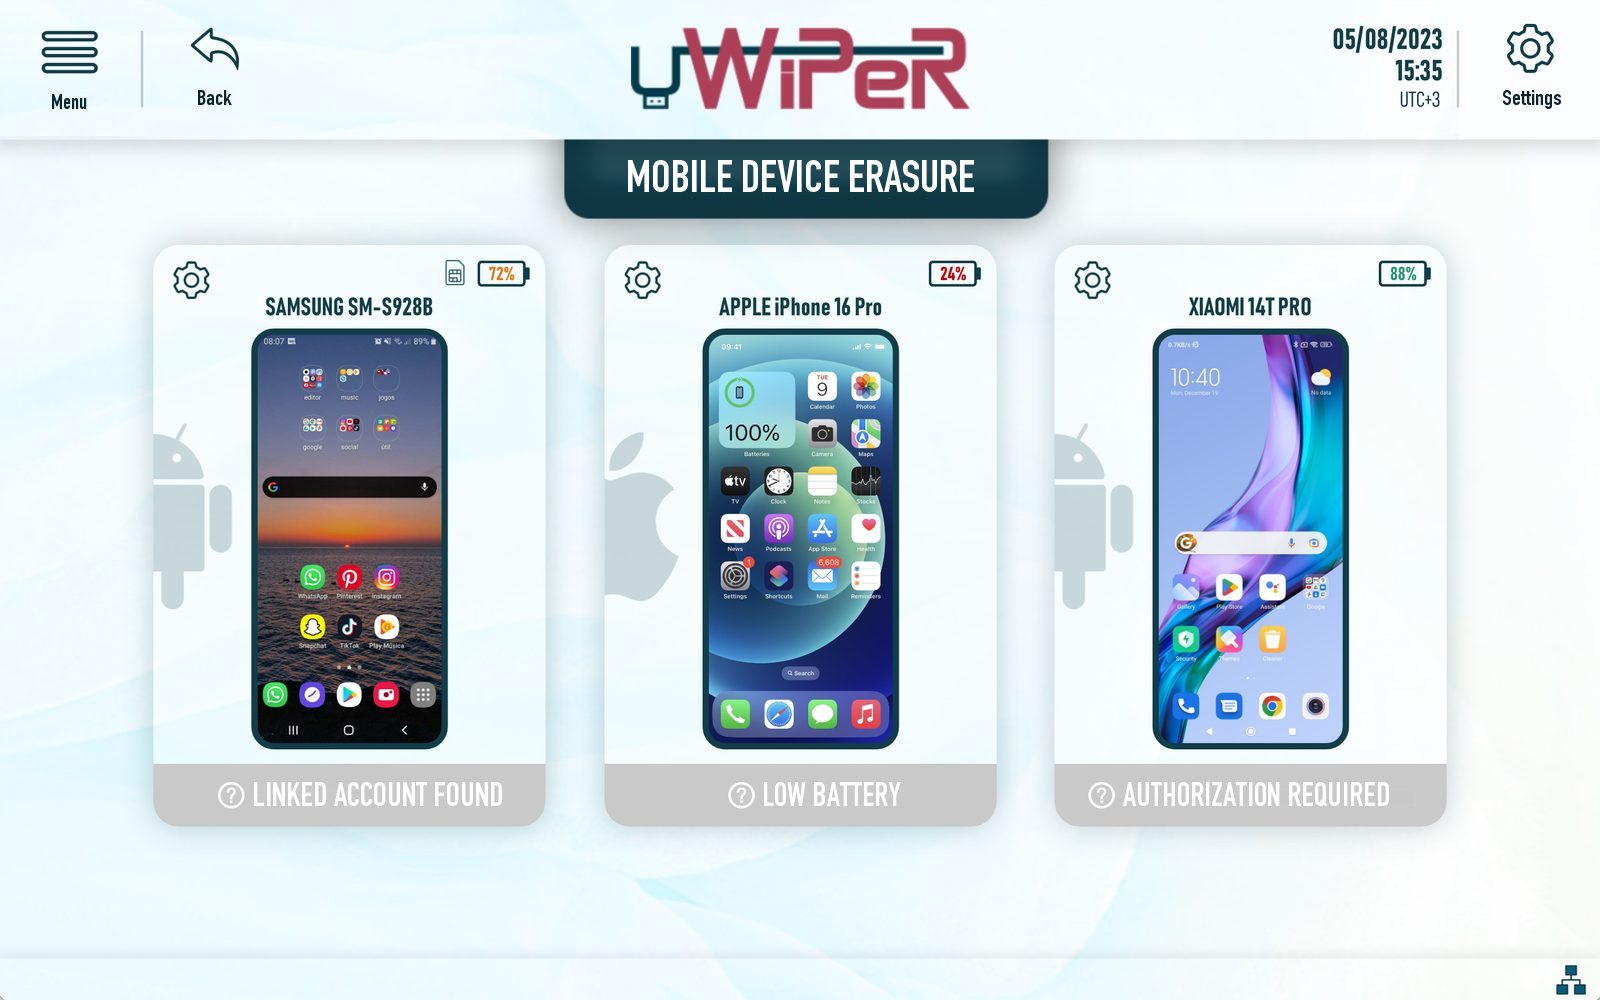
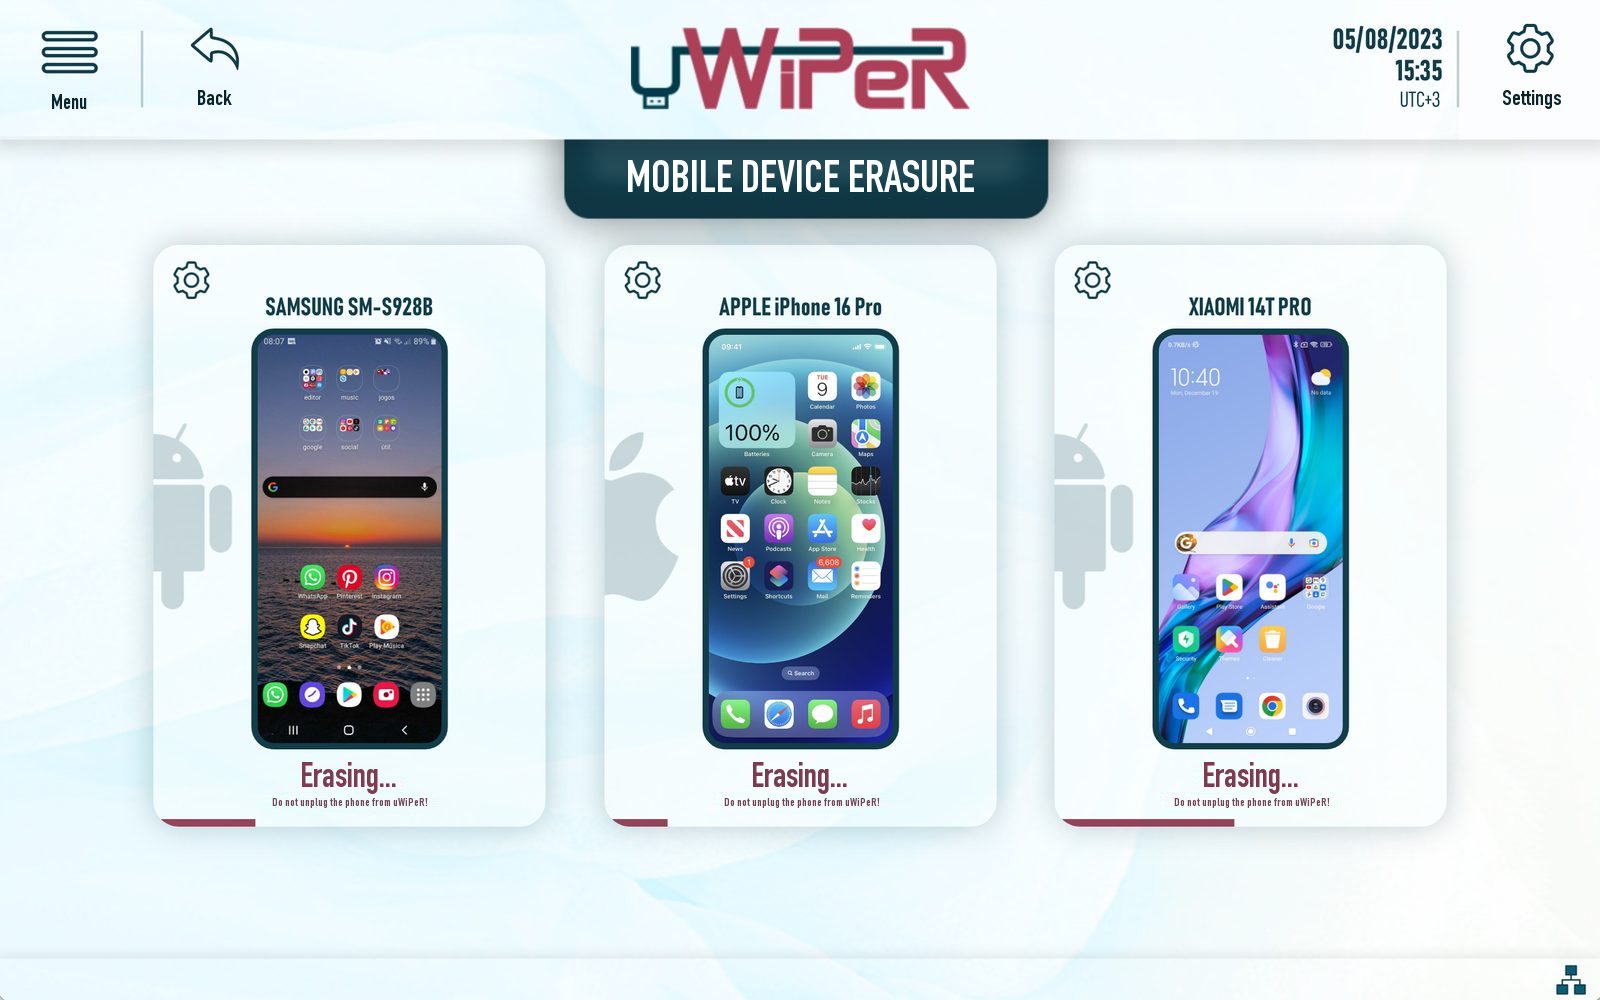
uWiPeR also tests the phone's hardware: touchscreen, cameras, microphone, sensors and more. The results go into the device report, so every phone leaves both clean and graded for reuse, resale or return.
Whether you answer to European or international rules, the question at the audit is the same. uWiPeR gives you the answer on paper.
The General Data Protection Regulation makes controllers responsible not only for deleting personal data, but for being able to demonstrate it.
People can ask for their personal data to be erased without undue delay, and the controller must do it.
The controller is responsible for compliance and must be able to demonstrate it.
Appropriate technical measures are required, including for media that is retired, returned or reused.
Information security management systems expect secure deletion to be a controlled, evidenced process, not a habit.
Information stored in systems, devices and media must be deleted when it is no longer required.
Before equipment is disposed of or reused, sensitive data must be removed or securely overwritten, and this must be verified.
Media sanitisation guidelines and sector rules such as PCI DSS and HIPAA expect a recognised method and a record.
The same record answers the GDPR auditor and the ISO 27001 assessor.
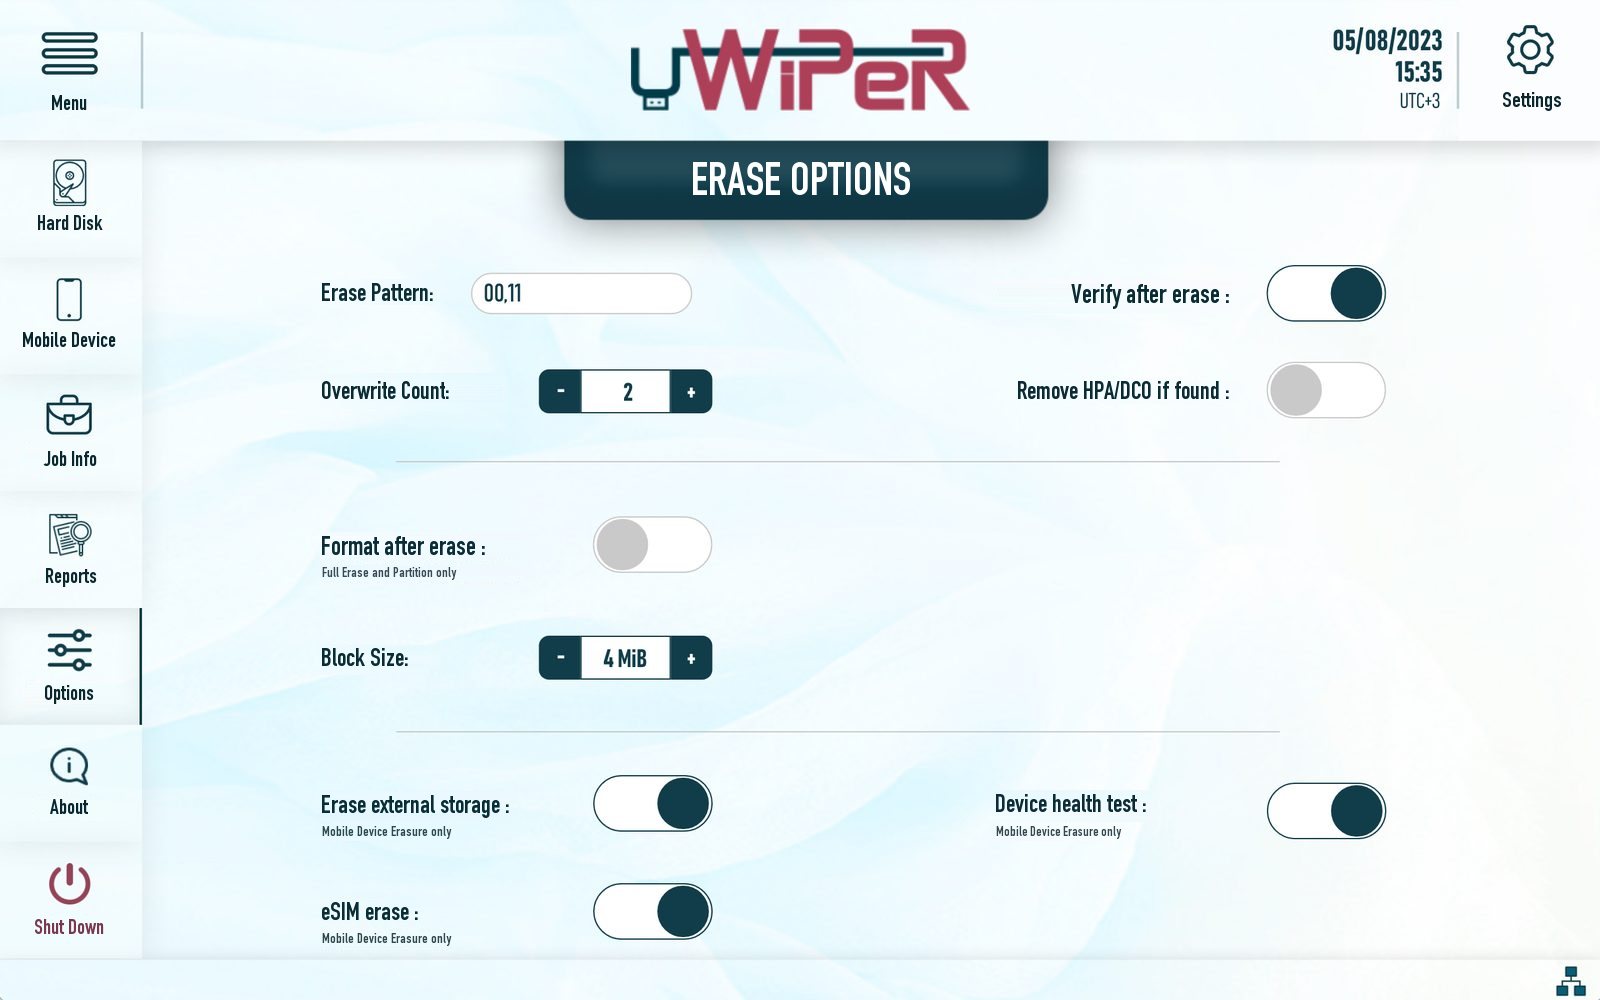
Choose the method your policy names. Each standard brings its own pattern, pass count and verification.
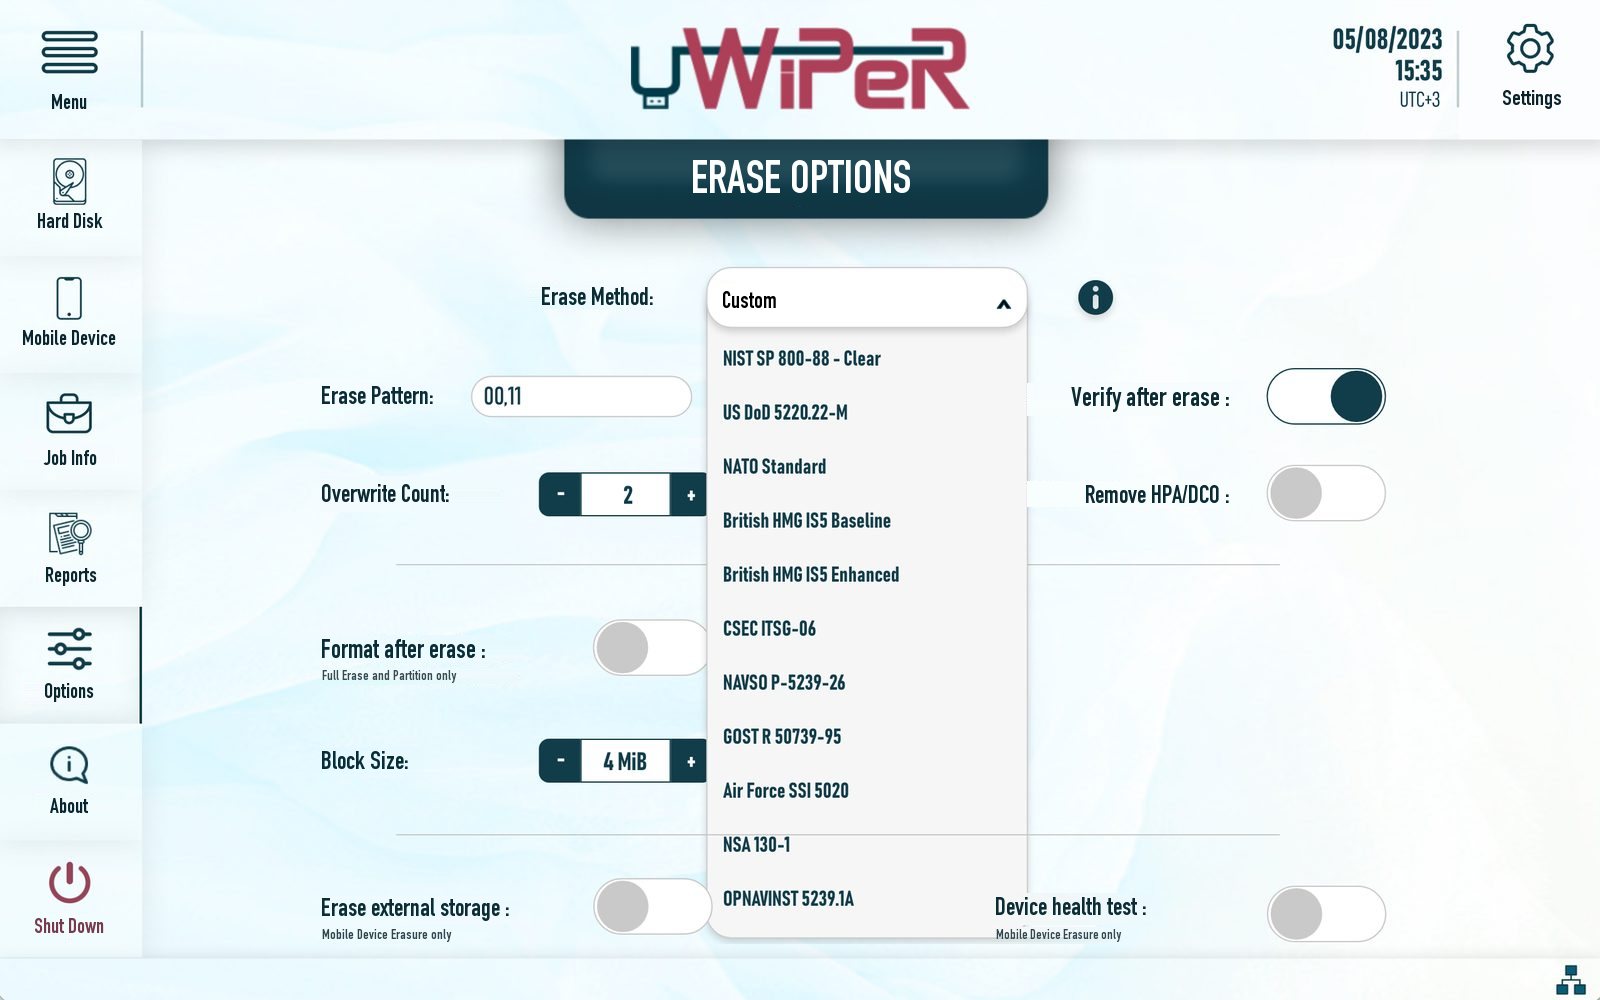
Large touch targets, clear status at every step, and the same flow for disks and phones.
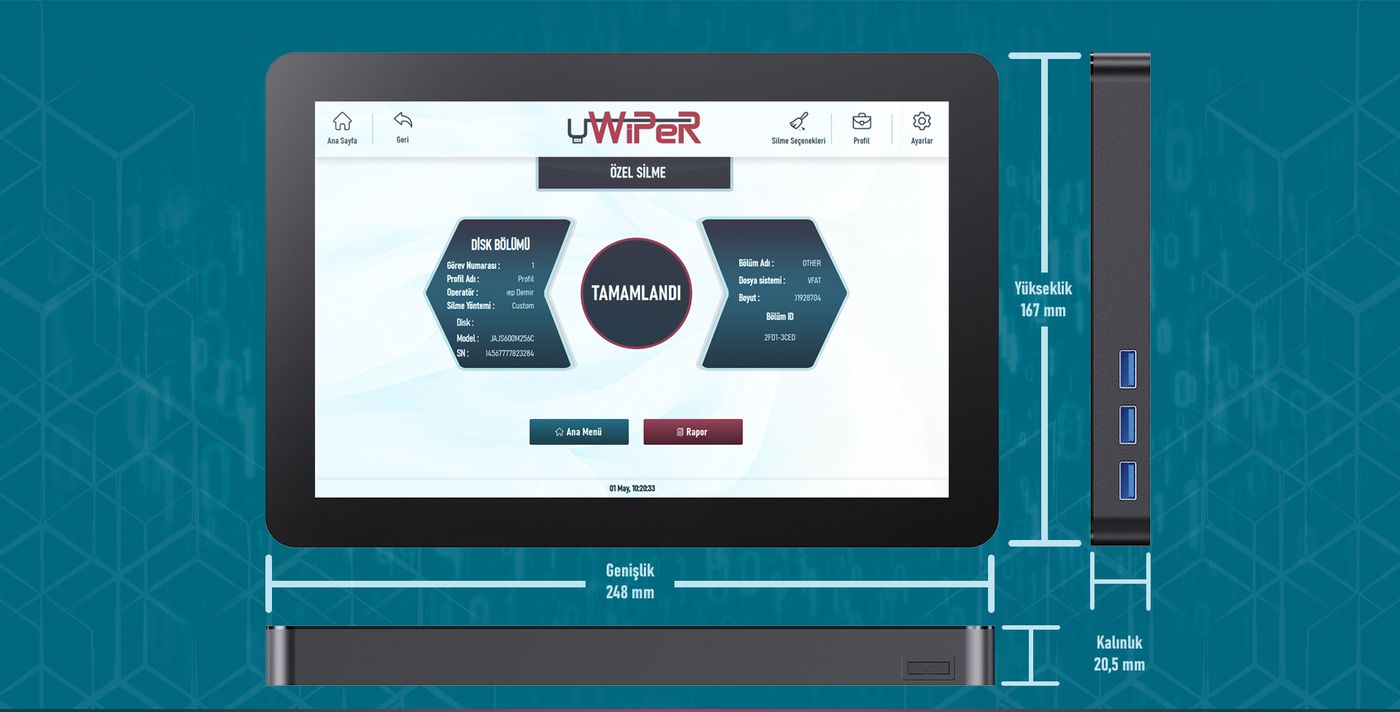 Aluminium body · fanless
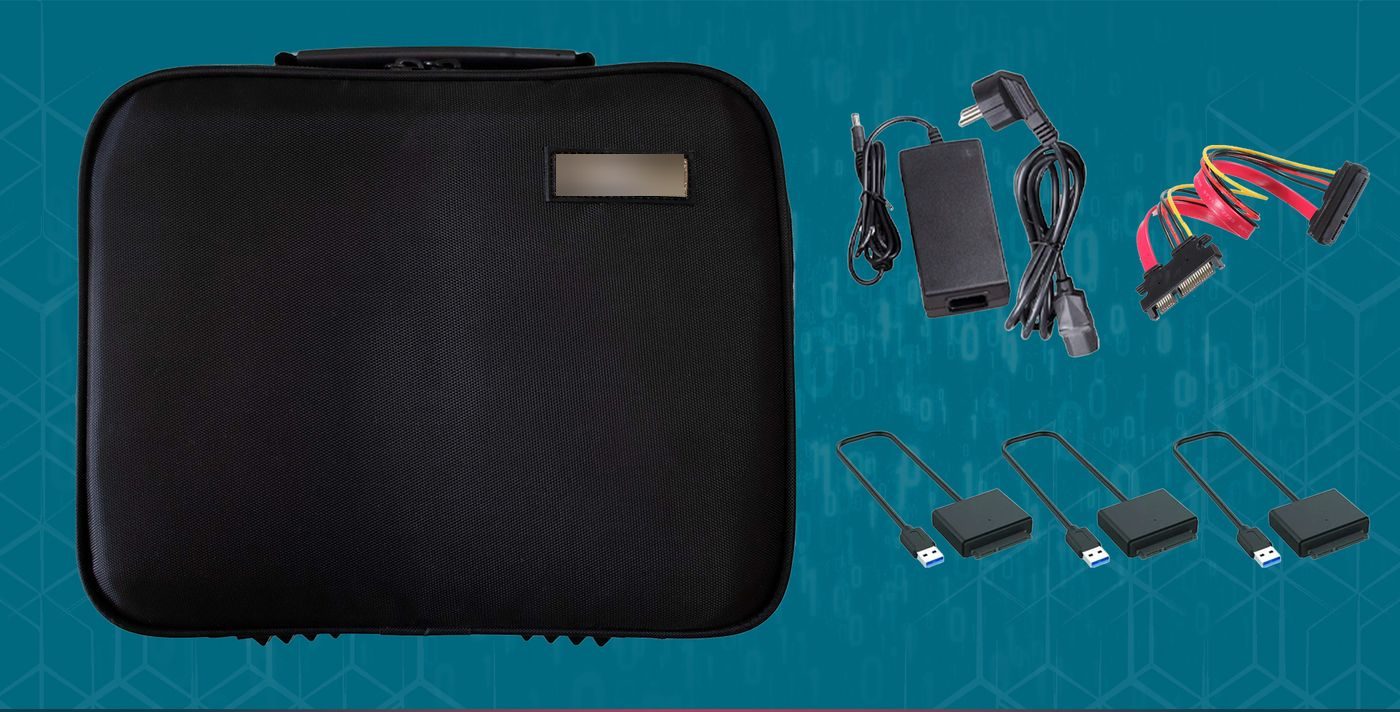
A fanless aluminium device with its own 10.1″ touchscreen. Carry it to the server room, the branch office or the client site in its case.
Tell us how many disks and phones you retire each month and which rules you answer to. We will show you uWiPeR in action.